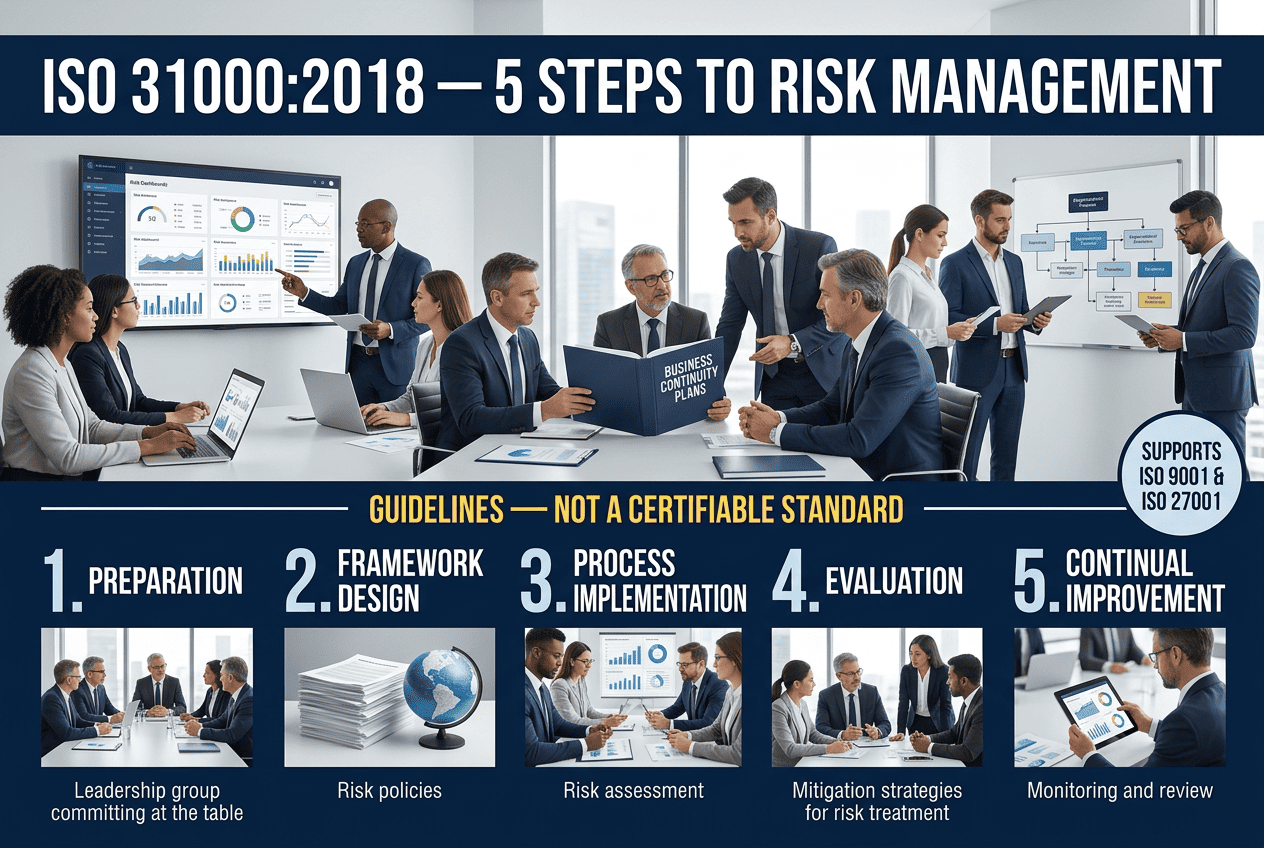
Direct Answer: ISO 31000:2018 is the international standard for risk management, but it provides guidelines, not certifiable requirements, so organisations cannot receive an accredited ISO 31000 certificate. What you can do is follow a 5-step route: Preparation (leadership buy-in, training, scope), Framework Design (policy, roles, integration), Process Implementation (context, risk assessment, treatment, monitoring), Evaluation (internal review or independent gap assessment) and Continual Improvement. Individuals can also earn professional credentials such as PECB ISO 31000 Risk Manager or the GSDC Certified ISO 31000:2018 Risk Manager. This guide explains each option, realistic timelines and how ISO 31000 supports certifiable standards like ISO 9001 and ISO 27001.
📅 November 2, 2026⏱ 15 min read✍️ GT Setu Editorial Team🔄 Updated regularly
2018
Current Edition (2nd Edition)
8
Risk Management Principles
5
Steps to Implementation
0%
GTsetu Broker Commission
ISO 31000 is the world’s best-known risk management standard. Published by the International Organization for Standardization (ISO), it gives any organisation, whatever its size, sector or ownership, a common vocabulary, set of principles, framework and process for managing risk. Risk is defined as the effect of uncertainty on objectives, which means it covers opportunities as well as threats: financial, operational, strategic, legal, reputational, environmental and cyber.
For manufacturers, distributors and cross-border traders, a sound risk management approach is increasingly a due diligence expectation from buyers, lenders and insurers. Unlike a certifiable standard, however, ISO 31000 is a guidance document. This article explains what that means in practice, how to implement it properly, and which credentials you can actually obtain. See our related guides on partnership evaluation criteria and risk allocation in cross-border deals to see how risk thinking applies to partner selection.
⚠️ Important: ISO 31000 Is Not Certifiable for Organisations
ISO 31000:2018 contains guidelines (it uses “should”, not “shall”), so there is no accredited organisation-level certificate. Be cautious of any provider offering an “ISO 31000 certificate” for your company: ask which accreditation body backs it. What is legitimate is (a) implementing the guidelines, (b) an independent conformity or gap assessment that states alignment, and (c) personal certification for your people. For standards that do carry accredited certificates, see our guides to ISO 9001 and ISO 27001.
📋 Who Is This Guide For?
Risk managers, compliance officers, quality and operations leaders, founders and procurement teams who want a structured, defensible approach to risk. It is relevant to manufacturers preparing for customer audits, distributors managing principal requirements, and anyone planning to combine ISO 31000 with a certifiable management system. See also supplier collaboration platforms and distributors and manufacturers.
SECTION 1
1 What Is ISO 31000 & Can You Get Certified?
⚖️ The Standard Explained
ISO 31000 (current edition ISO 31000:2018, which replaced the 2009 version) sets out principles, a framework and a process for managing risk. It is generic and industry-neutral, shorter and more strategic than the 2009 edition, and written to be integrated into governance and decision-making rather than run as a separate programme. Because it offers guidance rather than auditable requirements, organisations cannot be certified to it. Instead, they demonstrate alignment through implementation, internal review and optional independent assessment, while professionals can be certified through training bodies.
📘
ISO 31000: Guidelines
Principles, framework and process for managing any type of risk. Used by organisations of every size and sector.
🧰
IEC 31010: Techniques
A companion standard describing risk assessment techniques such as FMEA, bow-tie analysis, scenario analysis and Monte Carlo simulation.
📖
ISO 31073: Vocabulary
Shared risk management terminology so that teams, auditors and partners use the same language.
🎓
Personal Credentials
Bodies such as PECB and GSDC certify individuals (Foundation, Risk Manager, Lead Risk Manager), not the organisation’s system.
SECTION 2
2 Key Benefits of Adopting ISO 31000
Even without an organisation-level certificate, a well-implemented ISO 31000 approach delivers benefits across the business. The value comes from better decisions, not from a certificate on the wall.
🎯
Better Decision-Making
Risk information feeds strategy, budgeting and project decisions, so leaders weigh uncertainty explicitly instead of relying on instinct.
Strategic
🛡️
Fewer Surprises & Losses
Proactive identification and treatment of risks reduces incidents, disruptions, claims and unplanned costs.
Operational
🔗
Stronger Supply Chain Confidence
A documented, repeatable risk approach reassures customers, principals, lenders and insurers during due diligence.
Partnership
📊
Consistent Risk Language
Common criteria and a shared vocabulary let departments compare and prioritise risks on the same scale.
Analytical
🧩
Foundation for Certifiable Standards
ISO 31000 underpins the risk-based thinking required by management system standards such as ISO 9001, ISO 14001, ISO 45001 and ISO 27001.
Compliance
🌱
Capturing Opportunity
Because risk includes positive effects of uncertainty, the process helps organisations pursue opportunities with eyes open.
Growth
SECTION 3
3 The 8 Principles of Risk Management
ISO 31000:2018 states eight principles that guide effective, efficient risk management. They explain why risk management should be designed the way it is, and auditors and assessors will look for evidence that they are reflected in practice.
🧩
1. Integrated
Risk management is part of all organisational activities, not a standalone exercise.
🏗️
2. Structured & Comprehensive
A structured, comprehensive approach contributes to consistent and comparable results.
🎛️
3. Customised
The framework and process are proportionate to the organisation’s context and objectives.
🤝
4. Inclusive
Appropriate, timely involvement of stakeholders leads to better awareness and informed risk management.
🔄
5. Dynamic
Risks emerge, change and disappear as context changes, so the approach must anticipate and respond.
📊
6. Best Available Information
Inputs draw on historical and current information, with awareness of limitations and uncertainties.
🧠
7. Human & Cultural Factors
Human behaviour and culture significantly influence every aspect of risk management.
📈
8. Continual Improvement
Risk management improves through learning and experience.
SECTION 4
4 Step 1: Preparation, Foundation & Planning
🏗️ Building the Foundation
Preparation ensures you start with the right knowledge, mandate and scope. Plan on roughly 2 to 6 weeks, depending on how much risk activity already exists in your organisation.
1.1
Get Trained on ISO 31000
Whoever leads the work should understand the principles, framework and process. A Foundation-level course, or the standard itself together with ISO 31073 vocabulary, is a sensible starting point.
1.2
Secure Leadership Commitment
The standard places strong emphasis on leadership and commitment. Top management should approve the policy, assign accountability and allocate resources. See company global expansion for how risk governance supports growth.
1.3
Define Objectives & Scope
Decide what you want risk management to achieve (resilience, customer assurance, better capital allocation) and where it applies: entire enterprise, business unit, project or supply chain.
1.4
Take Stock of Existing Practices
Most organisations already manage risk informally through insurance, health and safety, quality checks or finance controls. Map these so you build on them instead of duplicating them.
1.5
Appoint a Risk Owner & Plan the Project
Name a risk coordinator or committee, set milestones and keep the plan simple. Ownership of individual risks should sit with the managers who can act on them.
1.6
Build Awareness
Explain why risk management matters and how it will help people do their jobs. Human and cultural factors are a core principle, so early engagement pays off.
💡 Pro Tip: Start With What Matters Most
Pilot the approach on one critical area, such as a key product line, a major supplier relationship or a new market entry, then extend. The same logic applies when building a B2B network: begin focused, then scale.
SECTION 5
5 Step 2: Framework Design
The ISO 31000 framework is about integrating risk management into governance, strategy, planning and reporting. It is organised around leadership and commitment, integration, design, implementation, evaluation and improvement. Documentation should be proportionate: enough to be consistent and auditable, not a bureaucratic burden.
Framework Element
What It Involves
Key Consideration
Risk Management Policy
A short statement of intent, approved by top management, that sets direction and commitment.
Link it to strategic objectives and communicate it to all staff and relevant partners.
Roles & Accountabilities
Who owns risks, who coordinates the process, who oversees and reports.
Risk owners should have authority and resources to act on risks.
Risk Criteria
The amount and type of risk the organisation may or may not take, plus scales for likelihood and consequence.
Align with risk appetite and keep scales consistent across departments.
Integration Plan
How risk management plugs into planning, project management, procurement, compliance and performance reviews.
Embedding it in existing processes is more sustainable than a parallel system.
Resources & Competence
People, training, tools and information systems that support the process.
A simple register or spreadsheet is enough to begin; scale tooling as maturity grows.
Communication & Reporting
Internal and external channels for sharing risk information.
Decide what goes to the board, management and external stakeholders, and how often.
Risk Register & Records
A record of identified risks, assessments, treatments, owners and review dates.
Keep it living: stale registers are a common finding in assessments.
💡 Documentation Best Practices
DO: use plain language and templates for the register, criteria and reports. DON’T: copy generic policies verbatim or create forms nobody uses. Templates speed things up, just as a proven template does when drafting manufacturer-distributor contracts, provided you tailor them to your context.
SECTION 6
6 Step 3: Implementing the Risk Process
The ISO 31000 process is iterative and is applied to strategic, operational, project and supply chain decisions alike. It runs alongside continuous communication and monitoring.
📢
Communication & Consultation
Engage internal and external stakeholders throughout so that perspectives, concerns and expertise inform every stage.
Continuous
🧭
Scope, Context & Criteria
Define the boundaries, understand the internal and external environment and set the criteria used to evaluate significance of risk.
Set-up
🔍
Risk Identification
Find, recognise and describe risks using workshops, checklists, historical data, supplier reviews and scenario thinking.
Assess
📐
Risk Analysis
Understand the nature, causes, likelihood and consequences of each risk. Qualitative, semi-quantitative or quantitative methods can be used; IEC 31010 lists techniques.
Assess
⚖️
Risk Evaluation
Compare analysis results with your criteria to decide whether the risk is acceptable or needs treatment, and in what priority.
Assess
🛠️
Risk Treatment
Select and implement options: avoid, take or increase risk for opportunity, remove the source, change likelihood or consequences, share (e.g. insurance, contracts) or retain.
Treat
📈
Monitoring, Review, Recording & Reporting
Track risks and controls, learn from incidents and document outcomes so decisions are traceable. See dispute resolution in international contracts for contract-level risk handling.
Ongoing
SECTION 7
7 Step 4: Evaluation & Internal Review
🔍 Verifying Your Approach
Because there is no certification audit, evaluation is how you prove it works. Measure the performance of the framework against its purpose, implementation plan, indicators and expected behaviours, and determine whether it remains suitable. An internal audit or an independent gap assessment against ISO 31000 is the closest equivalent to a certification audit.
📋
Define Indicators
Track measures such as risks reviewed on schedule, treatment actions closed, incidents against risk appetite and quality of risk reports.
👤
Use Independent Reviewers
Internal auditors or an external assessor should be impartial and not review their own work.
🧪
Run a Gap Assessment
Compare current practice with the principles, framework and process, rating each element and listing actions.
🗣️
Test Culture & Behaviour
Interview managers and staff: do they actually use the process in decisions, or only update the register before reviews?
📑
Obtain an Assessment Statement
Some firms provide a conformity or maturity assessment report. Treat it as an attestation of alignment, not an accredited certificate.
🏛️
Report to Leadership
Management review should consider results, emerging risks and resource needs, closing the loop with top management.
SECTION 8
8 Step 5: Improvement, Assessment & Professional Certification
Continual improvement turns evaluation results into updates to the framework, criteria and process. This is also the stage at which you decide what external recognition makes sense: an independent assessment for your organisation and professional certification for your people.
Route
What You Receive
Key Notes
Self-Assessment / Internal Audit
Internal report of conformity and improvement actions.
Lowest cost; valuable but carries less external credibility.
Independent Gap / Maturity Assessment
Written assessment of alignment with ISO 31000 from a consultancy or training body.
Not an accredited certificate. Check the assessor’s credentials and be transparent in how you describe the result.
PECB ISO 31000 Credentials
Individual certificates, e.g. Foundation, Risk Manager and Lead Risk Manager.
Training course plus exam; some levels require experience.
GSDC Certified ISO 31000:2018 Risk Manager
Individual professional credential for risk practitioners.
Validates personal competence in the 2018 guidelines.
Certifiable Standards Using Risk Thinking
Accredited organisation certificates, e.g. ISO 9001, ISO 14001, ISO 22301, ISO 27001, ISO 45001.
ISO 31000 provides the risk method; these standards provide the auditable certificate.
💡 Be Honest in Your Marketing
Say “aligned with ISO 31000” or “our risk management follows ISO 31000:2018” rather than “ISO 31000 certified” for the organisation. Individual staff can accurately say they hold a named ISO 31000 professional certification. Clear wording protects credibility with sophisticated buyers, who will check, as they would using business verification methods.
SECTION 9
9 Costs & Timeline: What to Expect
Because there is no registrar and no fixed audit schedule, costs and timelines depend mainly on your risk maturity, size and how much external help you buy. The figures below are indicative planning ranges, not quotes; always confirm current pricing with training providers and consultants.
Factor
Impact on Cost
Impact on Timeline
Organisation Size
Larger and multi-site organisations need more workshops, training and reporting effort.
Most value comes from training the people who run the process, getting leadership involved early and using simple tools consistently. Spend on external assessment only when a customer, lender or regulator will actually value it. Evaluate any provider as you would any B2B engagement, using partnership evaluation criteria.
SECTION 10
10 ISO 31000 and Other ISO Standards
ISO 31000 is often the common risk thread running through an organisation’s management systems. Using one risk method across them avoids duplication and gives leadership a single view of exposure. Explore the certifiable standards below, each with its own step-by-step guide.
Sector-specific risk management for medical devices, closely related in approach to ISO 31000.
SECTION 11
11 Common Mistakes & How to Avoid Them
🏷️
Chasing a Non-Existent Certificate
Paying for an “organisation certificate” that no accreditation body backs.
Avoid: Ask who accredits the issuer. Aim for demonstrable alignment and certified professionals instead.
📋
Risk Register as a Paper Exercise
A long list that is never reviewed or tied to decisions.
Avoid: Link risks to objectives, owners and review dates, and use them in planning and reporting.
🏛️
Weak Leadership Involvement
Risk management delegated entirely to a junior coordinator.
Avoid: Make leaders accountable for risk appetite, criteria and review of top risks.
🧩
Running It as a Separate Silo
A parallel process that does not touch strategy, projects or procurement.
Avoid: Integrate into existing planning cycles and supplier onboarding. See risk allocation in contracts.
🎓
Ignoring Culture & Training
Staff who do not understand or trust the process will not report risks.
Avoid: Train at every level and reward early reporting. Consider structured global partner service models for onboarding.
🔄
Never Updating the Approach
Context changes but criteria, scales and risks stay frozen.
Avoid: Schedule regular framework reviews and trigger reviews on major changes, in line with the “dynamic” principle.
SECTION 12
12 How GTsetu Supports Your Risk Management Journey
🔗 GTsetu, Verified B2B Platform
Reduce Partner Risk with Verified Counterparties
Supplier and partner risk is one of the most important risk categories for manufacturers and distributors. GTsetu helps you manage it by connecting you with verified companies, with confidentiality and secure collaboration built in. Our platform provides:
✅
Verified Company ProfilesEvery company is verified on 6 key data points (Name, Address, Registration Number, Company Status, Company Type, Date of Incorporation) using government tie-ups, reducing counterparty risk.
🕵️
Anonymous DiscoveryBrowse verified partner profiles without revealing your identity until you are ready to engage, protecting your sourcing strategy.
📄
Built-In NDA WorkflowDigital mutual NDA with timestamped signatures, activated before sensitive commercial or technical data is exchanged.
🔐
Encrypted Document WorkspaceAES-256 encryption at rest, TLS in transit, role-based access controls and a full audit trail for safe exchange of risk-sensitive documents.
🚫
Zero Broker CommissionGTsetu charges zero commission on any partnership formed, so the commercial value stays between you and your verified partner.
🌏
Global Network of Verified PartnersAccess verified manufacturers, distributors and suppliers across 100+ countries to diversify your supply base and reduce concentration risk.
No. ISO 31000:2018 provides guidelines rather than requirements, so it is not designed for third-party certification of organisations, and accredited certification bodies do not issue an ISO 31000 organisation certificate. Organisations can instead implement the framework, run an internal or independent conformity (gap) assessment, and certify their people through professional programmes. If you need an accredited certificate, consider ISO 9001 or ISO 22301.
QWhat are the main steps to implement ISO 31000?
The five practical steps are: (1) Preparation: secure leadership commitment, train key people and define scope. (2) Framework design: establish risk policy, roles, resources and integration into governance. (3) Process implementation: apply the risk process of context, assessment, treatment, monitoring and reporting. (4) Evaluation: measure performance and run an internal review or gap assessment. (5) Improvement: adapt the framework and, if wanted, obtain an independent conformity assessment or certify your professionals. As with any distributor network, start with a solid foundation and build methodically.
QWhich ISO 31000 certifications are available for individuals?
Several training bodies offer personal certifications, for example PECB (ISO 31000 Foundation, Risk Manager and Lead Risk Manager) and the GSDC Certified ISO 31000:2018 Risk Manager. These certify an individual’s competence in the guidelines, not the organisation’s management system. Check each provider’s current prerequisites, exam format and fees before enrolling.
QHow long does it take to implement ISO 31000?
Timelines vary with size, risk maturity and existing governance. As an indicative guide, small organisations often need 3 to 6 months, medium organisations 6 to 9 months, and large or multi-site organisations 9 to 18 months, since there is no fixed audit schedule. Individual training courses typically take a few days.
QHow is ISO 31000 different from ISO 9001 or ISO 27001?
ISO 9001 and ISO 27001 are management system standards with auditable requirements and accredited certification. ISO 31000 is a guidance standard focused on how to manage risk of any kind, and it is generic and industry-neutral. Its principles can support the risk-based thinking required by certifiable standards, including ISO 14001 and ISO 45001.
QWhat is the difference between ISO 31000 and ISO 31010?
ISO 31000 sets out principles, a framework and a process for managing risk. IEC 31010 is a companion standard that describes techniques for risk assessment, such as brainstorming, FMEA, bow-tie analysis and Monte Carlo simulation. ISO 31073 provides the shared risk management vocabulary. For sector-specific risk management, see ISO 14971 for medical devices and ISO 26262 for automotive functional safety.
Connect with verified manufacturers, distributors and suppliers on GTsetu: compliance-backed verification, anonymous discovery, built-in NDA workflows and zero broker commissions.
They represents the product, and research team behind GTsetu, a global B2B collaboration platform built to help companies explore cross-border partnerships with clarity and trust. The team focuses on simplifying early-stage international business discovery by combining structured company profiles, verification-led access, and controlled collaboration workflows.
With a strong emphasis on trust, and disciplined engagement, Team GTsetu shares insights on global trade, partnerships, and cross-border collaboration, helping businesses make informed decisions before entering deeper commercial discussions.