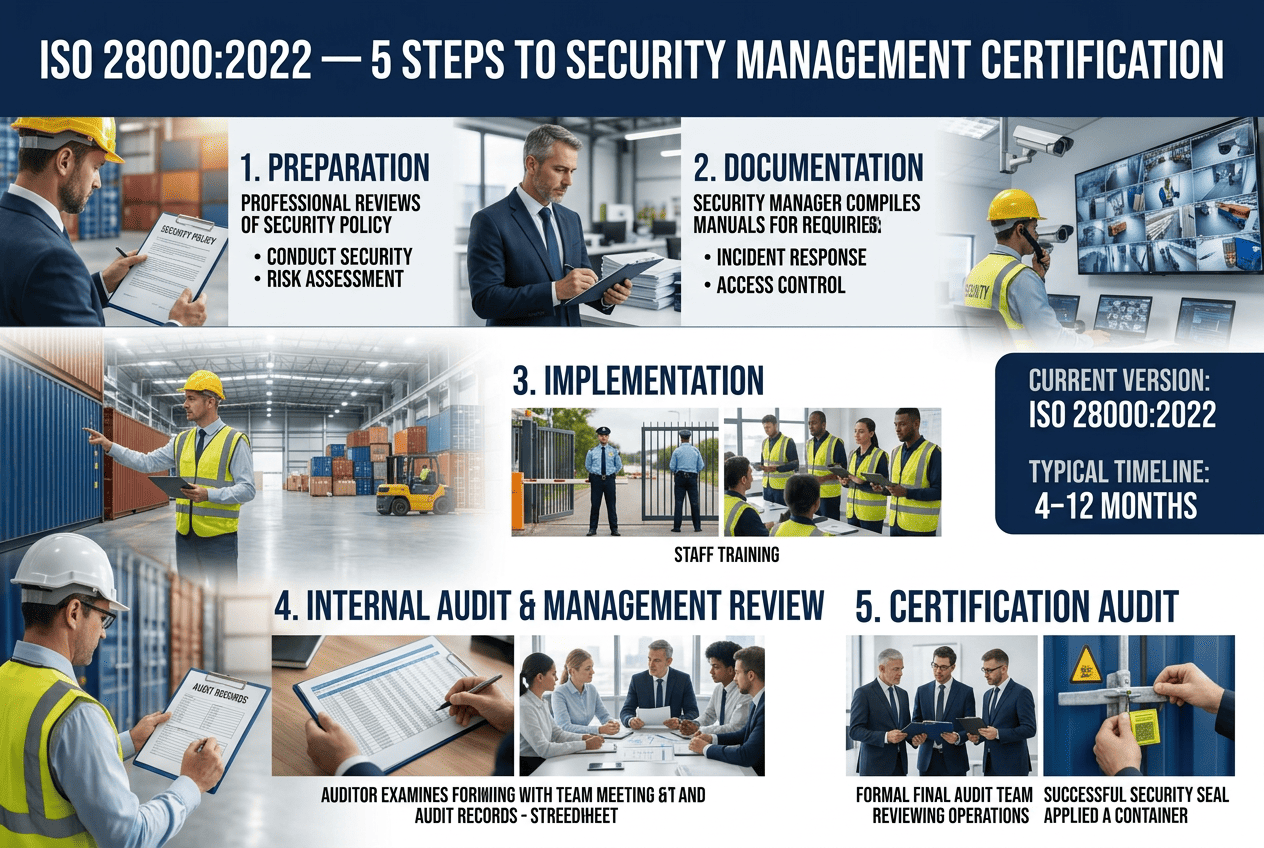
Direct Answer: ISO 28000 is the international standard for Security Management Systems (SMS). The current edition, ISO 28000:2022, specifies requirements for managing security-related risks across your organisation and its supply chain. Getting certified involves a 5-step process: Preparation (management support, scope definition, gap analysis), Documentation (security policy, security risk assessment, procedures, records), Implementation (rolling out controls, training staff, preparing for incidents), Internal Audit & Management Review (verifying that the system works), and Certification Audit (a two-stage audit by an accredited certification body, followed by certificate issuance). Most organisations take roughly 4–12 months depending on size, number of sites and existing management-system maturity. This guide walks you through every step, with practical tips for a smooth certification journey.
📅 November 2, 2026⏱ 16 min read✍️ GT Setu Editorial Team🔄 Updated regularly
2022
Current Edition (ISO 28000:2022)
5
Key Steps to Certification
3 Yrs
Certificate Validity Cycle
0%
GTsetu Broker Commission
ISO 28000 is the international management system standard for security. Published by the International Organization for Standardization (ISO), it sets out requirements for a security management system that helps organisations identify, assess and treat security-related risks – from theft, tampering and unauthorised access to sabotage and other deliberate threats. Originally developed in 2007 specifically for supply chains, the standard was fully revised in March 2022 and now applies to every aspect of an organisation’s security, including the supply chain activities that move goods, data and people between partners.
For manufacturers, distributors, freight forwarders, warehouse operators and exporters, ISO 28000 certification is a strong signal to buyers, carriers, ports and regulators that cargo, facilities and information are protected throughout the value chain. This guide covers the complete certification process – from initial preparation through to the final certification audit – and provides practical advice for a smooth journey. See our related guides on partnership evaluation criteria and business verification to understand how ISO 28000 fits into partner due diligence. If you are new to management system certification, start with our guide on how to get ISO 9001 certification, since ISO 28000:2022 follows the same harmonised structure.
📋 Who Is This Guide For?
This guide is written for security managers, supply chain and logistics directors, quality managers, business owners and anyone responsible for implementing or maintaining a Security Management System. It covers both the DIY approach (using templates and internal resources) and the consultant-led route. It is equally relevant for manufacturers seeking to reassure customers about cargo and facility security, and for distributors and logistics providers who need to demonstrate security controls to their principals. For related partnership structures, see our guides on supplier collaboration platforms and distributors and manufacturers.
SECTION 1
1 What Is ISO 28000 & Why Get Certified?
🛡️ The Standard Explained
ISO 28000:2022, titled “Security and resilience – Security management systems – Requirements”, specifies requirements for a security management system, including aspects relevant to the supply chain. It is a certifiable standard, applicable to organisations of any type, size and industry. The 2022 edition replaced ISO 28000:2007, adopted the harmonised structure (Annex SL) shared with ISO 9001, ISO 14001 and ISO 22301, and aligns security risk management with the principles of ISO 31000. It is built around a Plan-Do-Check-Act (PDCA) cycle: understand your context and security risks, put controls in place, monitor and audit them, and keep improving.
🌐
Internationally Recognised Framework
ISO 28000 gives logistics partners, carriers, ports and buyers a common language for security. It is used across industries and borders, which makes it valuable for exporters and global supply chains.
🚢
Beyond the Supply Chain
The 2022 revision removed the supply-chain-only limitation. The standard can now be used across all aspects of organisational security – facilities, people, information and goods in transit.
⚖️
Risk-Based by Design
Security controls are selected on the basis of an assessed risk profile rather than a fixed checklist, so you invest where threats are real and avoid over-engineering where they are not.
🤝
Customer & Partner Confidence
Certification by an accredited body is independent evidence that your security arrangements are systematic, tested and continually improved – a strong differentiator in tenders and partner onboarding.
SECTION 2
2 Key Benefits of ISO 28000 Certification
ISO 28000 certification delivers benefits across operational, commercial and strategic dimensions. The standard itself highlights improved security and resilience, systematised management practices, enhanced credibility and brand recognition, better compliance processes and the ability to benchmark against internationally recognised criteria.
10
Clauses in ISO 28000:2022, following the harmonised ISO management system structure
PDCA
Plan-Do-Check-Act model driving continual improvement of security performance
3 + 1
Three-year certificate cycle with annual surveillance audits in between
🏷️
Enhanced Credibility & Market Access
Independent certification signals to customers, carriers and regulators that you manage security systematically. It can help you qualify for tenders and logistics contracts that ask for evidence of supply chain security.
Commercial
🔒
Reduced Losses from Theft & Tampering
Structured threat identification, access control and incident handling reduce exposure to cargo theft, pilferage, counterfeiting and product tampering – and the claims, delays and reputational damage that follow.
Operational
🔗
Stronger Supplier & Partner Assurance
The standard asks you to manage security risks arising from external providers, which pushes consistent expectations through your supply chain and makes partner audits easier.
Partnership
🧩
Integration with Other Management Systems
Because ISO 28000:2022 shares its structure with other ISO standards, it integrates smoothly with quality, environmental, continuity and information security systems – sharing documents, audits and reviews.
Integration
👥
Security Awareness & Clear Responsibilities
Defined roles, training and communication make security everyone’s job rather than a guard-house function, reducing human error and insider-related risks.
People
📋
Compliance & Resilience
A documented system for identifying legal and other requirements, assessing risks and preparing for security incidents improves regulatory compliance and the ability to recover quickly when something goes wrong.
Compliance
SECTION 3
3 ISO 28000:2022 Structure & Core Requirements
ISO 28000:2022 is divided into ten clauses. Clauses 1–3 (scope, normative references, terms and definitions) are introductory; clauses 4–10 contain the requirements that an auditor will assess. If you have implemented ISO 9001, ISO 14001 or ISO 22301, the architecture will feel familiar.
🏢
4. Context of the Organisation
Understand internal and external issues, interested parties and their requirements, define the scope of the SMS, and establish the system itself – including its interaction with supply chain activities.
🏛️
5. Leadership
Top management must demonstrate commitment, establish a security policy, and assign roles, responsibilities and authorities for security management.
🗺️
6. Planning
Address risks and opportunities, determine and assess security-related risks, set security objectives and plan how to achieve them, and plan changes to the system.
🧰
7. Support
Provide resources, ensure competence and awareness, manage communication, and control documented information needed for the SMS.
⚙️
8. Operation
Plan and control operational processes, carry out security risk assessment and treatment, implement controls, and prepare for and respond to security incidents and emergencies.
📊
9. Performance Evaluation
Monitor, measure, analyse and evaluate security performance; conduct internal audits; and hold management reviews at planned intervals.
📈
10. Improvement
Manage nonconformities and corrective actions, and continually improve the suitability, adequacy and effectiveness of the security management system.
📋 Moving from ISO 28000:2007 to ISO 28000:2022
If your organisation held a certificate to the 2007 edition, the transition period set for moving to the 2022 edition has ended, and certification is now to ISO 28000:2022. The 2022 edition adopts the harmonised structure, introduces more explicit requirements on leadership, context and performance evaluation, and ties security risk assessment to ISO 31000 principles. Confirm your exact position and any outstanding deadlines directly with your certification body.
SECTION 4
4 Step 1: Preparation – Foundation & Planning
🏗️ Building the Foundation
The preparation phase sets the foundation for your entire ISO 28000 project. The goal is to ensure you have the knowledge, resources and management support in place before you begin the detailed work of risk assessment, documentation and implementation. For a small, single-site organisation this phase may take a few weeks; multi-site or multi-country operations will take longer.
1.1
Get Trained on ISO 28000
Whoever leads the project needs a working understanding of ISO 28000:2022 and its link to ISO 31000 risk management. Training providers such as PECB offer foundation, implementer and lead auditor courses. If you use a consultant, make sure you understand the key concepts so you remain an informed client.
1.2
Secure Executive Support
Top management must own the security policy, provide resources and visibly support the project. Present the business case in concrete terms: customer requirements, incident exposure, tender eligibility and insurance or compliance drivers. See our guide on company global expansion for context on how security and compliance support growth.
1.3
Define Context, Interested Parties & Scope
Identify who has expectations of your security arrangements (customers, carriers, customs and port authorities, insurers, regulators, employees) and decide the boundaries of the SMS: which sites, products, processes and supply chain activities are included. A clearly defined scope is one of the first things an auditor reviews. See partnership evaluation criteria for a framework that also helps with scope decisions.
1.4
Conduct a Gap Analysis
Compare your current security practices – access control, perimeter protection, cargo handling, vetting, incident response – against the requirements of ISO 28000:2022. The result shows what already exists, what needs strengthening and how large the project really is. Organisations that already run ISO 9001, ISO 22301 or ISO 27001 often find substantial overlap.
1.5
Create a Simple Project Plan
Set milestones, owners and target dates, and appoint a security management representative responsible for the system. Keep the plan simple and visible: a clear sequence of risk assessment, documentation, rollout, internal audit and certification audit is enough for most organisations.
1.6
Generate Employee Awareness
Explain early why the organisation is pursuing certification, how it protects staff, customers and jobs, and what will change day to day. Security succeeds only when employees – warehouse staff, drivers, office teams and contractors alike – understand and follow the rules.
💡 Pro Tip: Start with Your Highest-Risk Site or Lane
For organisations with multiple facilities or trade lanes, consider a phased approach. Pilot the SMS at the site or route with the greatest exposure, learn from the experience and then extend the scope. This reduces risk and lets you refine your approach with real-world feedback. The same principle applies when building a B2B network – start focused, then scale.
SECTION 5
5 Step 2: Documentation – Building Your SMS
ISO 28000:2022 requires documented information that is necessary for the effectiveness of your security management system. The goal is documentation that is useful, proportionate and tailored to your organisation – not a bureaucratic burden. The centrepiece of this step is the security risk assessment and treatment process, which determines which controls you actually need.
Document Type
Description
Key Consideration
Security Policy
A statement of management’s commitment to security, appropriate to the organisation, providing a framework for objectives and including a commitment to meet requirements and improve continually.
Keep it concise and specific. It must be available as documented information, communicated internally and available to interested parties as appropriate.
Scope Statement
Defines the boundaries and applicability of the SMS: sites, activities, products, services and supply chain stages covered.
State clearly what is in and out of scope and why. Auditors use it to plan the audit.
Security Objectives & Plans
Measurable security objectives consistent with the policy, with plans stating what will be done, by whom, with what resources and by when.
Examples: reduce cargo loss incidents by a set percentage, achieve 100% completion of security awareness training, close all high-risk findings by a target date.
Security Risk Assessment & Treatment
The method and results for identifying security threats and vulnerabilities, analysing and evaluating risks, and selecting treatments and controls.
Use a consistent, repeatable method aligned with ISO 31000 principles. Record criteria, results and decisions, and review whenever context changes.
Legal & Other Requirements Register
A list of applicable laws, regulations, customer requirements and voluntary programmes affecting your security arrangements.
Include customs, transport, trade-security and customer-contract obligations, and assign ownership for keeping it current.
Operational Procedures & Work Instructions
Documented controls for access management, visitor and driver handling, seal and container control, cargo handling, personnel screening, supplier security and incident response.
Write for the people who do the work. Use checklists, flowcharts and photos where they help; avoid duplicating content across documents.
Emergency Preparedness & Response Plans
Plans describing how the organisation will respond to security incidents such as break-ins, tampering, cargo theft or threats, including roles, communication and recovery.
Test the plans through drills or exercises and keep records of the results.
Records
Evidence of competence, training, monitoring results, incidents, internal audits, management reviews and corrective actions.
Records must be legible, retrievable and protected. They are a primary focus of every audit.
💡 Documentation Best Practices
DO: Reuse what you already have – existing site security procedures, quality system documents and continuity plans. Write in your company’s own language, use diagrams and keep each document owned by a named role.
DON’T: Copy generic templates without tailoring them, publish sensitive security details to people who do not need them, or create documents that add no operational value. Treat the risk assessment and security plans as controlled, need-to-know information.
Consider templates – a well-built template set, with clear customisation instructions, saves time and reduces omissions. This approach also works when drafting manufacturer-distributor contracts – start from a proven structure and tailor it.
SECTION 6
6 Step 3: Implementation – Rolling Out Your SMS
Implementation turns your documented system into daily practice. This phase introduces procedures to the workforce, puts physical, procedural and technical controls in place, and builds the habits and records an auditor will expect to see. Aim for security that is embedded in normal operations rather than bolted on.
📢
Communicate the Security Policy
Top management should explain the policy, why it matters and how each role contributes. Staff and relevant contractors must be aware of the policy and their responsibilities within the SMS.
Leadership
🎓
Train & Verify Competence
Provide role-based training for security staff, supervisors, drivers, warehouse teams and administrators, and keep records of competence. Short, practical sessions work better than long presentations.
Training
🚪
Implement Risk Treatments & Controls
Put the controls selected in your risk treatment plan into operation: access control, CCTV and alarms where justified, key and seal management, cargo checks, personnel screening and secure handover points.
Controls
🔗
Manage Suppliers & Service Providers
Apply security expectations to carriers, subcontractors and other external providers through contracts, questionnaires, audits or certification evidence. Keep records of due diligence.
Supply Chain
🚨
Prepare for & Practise Incident Response
Run drills for scenarios such as unauthorised entry, seal tampering or cargo theft. Record what worked, what did not and what you changed afterwards.
Resilience
📁
Monitor, Measure & Keep Records
Track the indicators you defined – incident counts, inspection results, training completion, response times – and keep the evidence. Auditors will ask for operating records, not just procedures.
Compliance
📣
Reap Early Commercial Benefits
While you are working towards certification, you can share your security programme with customers and partners, and use your progress in questionnaires and tenders where the rules allow.
Commercial
SECTION 7
7 Step 4: Internal Audit & Management Review
🔍 Verifying Your SMS
ISO 28000:2022 requires organisations to conduct internal audits at planned intervals and top management to review the system. Internal audits check whether the SMS conforms to your own requirements and to the standard, and whether it is effectively implemented and maintained. Both the audit and the management review must be completed – with findings addressed – before you ask a certification body to assess your system.
📋
Set Up the Audit Programme
Define frequency, methods, responsibilities, criteria and reporting. Base the programme on the importance of processes and the results of previous audits, and make sure every clause and site in scope is covered.
👤
Appoint Objective Auditors
Auditors must be objective and impartial and must not audit their own work. Small organisations may use trained staff from another department or an external auditor.
🎓
Train Your Auditors
Auditors should understand ISO 28000:2022, security risk concepts and audit techniques. Internal auditor or lead auditor training gives them confidence and consistency.
🔄
Audit Operations, Not Just Paperwork
Walk the site, observe gates, loading bays and storage areas, interview staff and check seals and logs. Security failures usually show up in practice before they show up in documents.
✅
Close Nonconformities
Record each nonconformity, find the root cause, implement corrective action and verify its effectiveness. Do this before the certification audit rather than leaving it for the auditor to find.
🏛️
Hold the Management Review
Top management reviews audit results, incident trends, risk changes, objectives, supplier performance and resource needs, and records decisions on improvement and changes to the system.
💡 Internal Audit as a Management Tool
An internal audit is more than a certification requirement. Use it to test your controls the way an adversary or a careless insider would – tailgating at doors, unsealed trailers, unverified drivers. The findings often reveal the cheapest, highest-impact improvements. The same principle applies to partnership evaluations – treat them as strategic tools, not just checkboxes.
SECTION 8
8 Step 5: Certification Audit – Getting Certified
The certification audit is the final step. It is conducted by an independent, third-party auditor from an accredited certification body. Audit requirements for these bodies are set out in the ISO/IEC 17021 family of standards, and the certification body should be accredited for ISO 28000 specifically. A successful audit results in an ISO 28000 certificate, normally valid for three years and subject to annual surveillance.
Audit Stage
What Happens
Key Focus
Stage 1 Audit (Readiness Review)
The auditor reviews your scope, security policy, risk assessment, documented information and overall readiness, and plans the Stage 2 audit.
Completeness of documentation, clarity of scope and risk method, and identification of gaps to fix before Stage 2.
Stage 2 Audit (On-Site Assessment)
The auditor visits your sites to confirm the SMS is implemented and effective. They interview staff, observe operations, inspect controls and review records.
Evidence that procedures are followed, controls operate as intended and objectives are being pursued.
Audit Report & Decision
The auditor reports findings. Major nonconformities must be corrected and verified; minor ones need an agreed corrective action plan. The certification body then decides whether to grant certification.
Overall conformity of the SMS with ISO 28000:2022.
Surveillance Audits
During the certificate cycle, the certification body carries out periodic (usually annual) surveillance audits on a sample of the system.
Ongoing conformity, closure of previous findings, handling of incidents and continual improvement.
Recertification Audit
Before the certificate expires, a recertification audit re-assesses the full system to renew certification for another cycle.
Sustained effectiveness and evolution of the SMS in line with changing risks and business needs.
💡 Preparing for the Certification Audit
Prepare your people and sites: Make sure staff can explain the security policy, their own responsibilities and how to report incidents. Check that gates, logs, seal records and training files are current and easy to retrieve. Staff should answer honestly and directly – there is no need to memorise scripts.
Select your certification body early: Choose an accredited body with sector experience, compare quotes and confirm that your customers recognise its certificates. See partnership evaluation criteria for a framework that also applies to certification body selection.
SECTION 9
9 Costs & Timeline: What to Expect
There is no single price for ISO 28000. Cost and timeline depend on the size and complexity of the organisation, the number of sites, the threat environment, existing management-system maturity and the resources you allocate. The figures below are indicative planning ranges only – always obtain written quotes from several accredited certification bodies.
Factor
Impact on Cost
Impact on Timeline
Organisation Size (Employees)
Larger workforces mean more audit days, more training and more documentation. Audit-day allocation is driven by headcount and complexity.
Small single-site: roughly 4–8 months Medium: roughly 6–12 months Large / multi-site: 12 months or more
Number of Sites & Locations
Each additional site adds audit time and travel, and may add control upgrades.
Multi-site rollouts extend implementation and audit schedules.
Security Risk Profile
High-value cargo, hazardous goods, high-risk trade lanes or sensitive facilities can require stronger controls and more detailed assessment.
Higher risk can lengthen the risk assessment and treatment phase.
Physical & Technical Upgrades
Fencing, lighting, CCTV, access control and tracking technology identified as risk treatments are often the largest variable cost.
Procurement and installation lead times can drive the critical path.
Existing Management Systems
If you already run ISO 9001, ISO 22301, ISO 27001 or ISO 45001, you can share documents, audits and reviews, lowering internal effort and enabling integrated audits.
Integration can shorten the timeline noticeably.
Consultant Involvement
Full consultant support adds cost; a DIY approach with training and templates costs less but needs more internal time.
Experienced support can accelerate documentation and readiness.
Certification Body Fees
Stage 1 and Stage 2 audits, annual surveillance audits and recertification are normally quoted separately.
Booking lead times vary; plan audit dates early.
📋 Budget Beyond the Audit
Many first-time applicants focus on audit fees and overlook the cost of staff time, training, physical security improvements and ongoing monitoring. Build these into your business case from the beginning. When evaluating consultants, software tools or training providers, use the same partnership evaluation criteria you would apply to any B2B engagement.
SECTION 10
10 How to Choose a Certification Body
The certification body (also called a registrar) is the independent organisation that audits your SMS and issues your ISO 28000 certificate. The choice affects cost, schedule and how widely your certificate is recognised. Resources such as the BSI ISO 28000 overview illustrate how major certification bodies describe their services and the standard itself.
🏛️
Accreditation Status
Choose a body accredited by a national accreditation body that is a member of the International Accreditation Forum (for example UKAS, ANAB, DAkkS, JAS-ANZ or NABCB), and check that ISO 28000 is explicitly within its accredited scope.
🏭
Sector Experience
Auditors who understand logistics, ports, warehousing, manufacturing or your sector will ask better questions and give more relevant improvement ideas.
📋
Market Recognition
Confirm that your customers, tender authorities and partners accept the body’s certificates, especially if you export to specific regions or serve regulated sectors.
💰
Cost & Transparency
Compare itemised quotes covering Stage 1, Stage 2, surveillance and recertification, plus travel. The cheapest quote is not always the best value.
🌐
Global & Multi-Site Capability
If you operate across countries, a body with consistent global coverage simplifies scheduling and reduces the risk of inconsistent audit approaches.
🤝
Relationship & Responsiveness
Assess communication during the quoting process. A good certification body is professional, impartial and clear about the process, while leaving consultancy to others to preserve independence.
💡 Certification Body Selection Checklist
Ask each body: Is ISO 28000 within your accreditation scope? Which auditors with experience in my sector would be assigned? How many audit days do you calculate for my scope, and on what basis? What is included in your fee? How do you handle nonconformities and certificate decisions? Can you provide references from similar organisations? Use the answers alongside your partnership evaluation criteria to make an informed choice.
SECTION 11
11 Common Mistakes & How to Avoid Them
⚖️
Treating Risk Assessment as a Formality
Copying a generic risk register means controls do not match your real threats, and auditors quickly see it.
Avoid: Assess your actual sites, routes, cargo and partners, using a documented method, and revisit the assessment when operations change.
🏛️
Lack of Management Commitment
If leadership treats ISO 28000 as a guard-force or compliance exercise, resources dry up and controls are not followed.
Avoid: Link security objectives to business outcomes and hold regular management reviews with real decisions and budgets.
🧱
Over-Reliance on Physical Security
Fences and cameras alone do not manage insider risk, documentation fraud or weak supplier controls.
Avoid: Balance physical, procedural, personnel and information controls, and verify them through audits and drills.
🔗
Ignoring Subcontractors & Carriers
Your security is only as strong as the weakest link in the chain – transport providers, warehouses and agents included.
Avoid: Define security requirements in contracts, assess critical providers and keep evidence. See global partner service models for structured partner programmes.
🎓
Inadequate Training & Awareness
Staff who do not understand why controls exist will bypass them, leading to nonconformities and real incidents.
Avoid: Provide role-specific training, explain the “why”, and test awareness through short drills and spot checks.
📊
Neglecting Corrective Action
Logging incidents and audit findings without root-cause analysis and follow-through leads to repeat failures.
Avoid: Verify that corrective actions work, track trends and feed lessons into the risk assessment. See risk allocation principles applied to security risks.
SECTION 12
12 ISO 28000 & Related Standards
ISO 28000 rarely stands alone. Because it shares the harmonised structure used across ISO management system standards, it can be combined with other certifications to build one integrated management system with shared policies, audits and reviews. Explore the guides below to see how each standard complements a security management system.
📋Quality
ISO 9001 – Quality Management
The foundation for consistent products and services. Shares the same harmonised structure, so documentation, internal audits and management reviews can be combined.
Food supply chains must manage deliberate contamination and tampering as well as accidental hazards – an area where food safety and security systems meet.
ISO 28000 is the first of a family of security management standards. Others in the series include ISO 28001 (best practices for implementing supply chain security, assessments and plans), ISO 28002 (resilience in the supply chain), ISO 28003 (requirements for bodies providing audit and certification) and ISO 28004 (implementation guidelines). Some of these were issued alongside the 2007 edition, so check the current status and edition of each on the ISO website before relying on it.
SECTION 13
13 How GTsetu Supports Your ISO 28000 Certification Journey
🔗 GTsetu – Verified B2B Platform
Connect with Verified Partners & Build Secure Supply Chains
ISO 28000 certification demonstrates that your organisation manages security risk systematically. GTsetu complements your certification by connecting you with verified manufacturers, distributors and suppliers, so the partners in your chain are as trustworthy as your own controls. Our platform provides:
✅
Verified Company Profiles
Every company on GTsetu is verified on 6 key data points (Name, Address, Registration Number, Company Status, Company Type, Date of Incorporation) using government tie-ups – complementing your supplier security due diligence.
🕵️
Anonymous Discovery
Browse verified partner profiles without revealing your identity until you’re ready to engage – protecting your sourcing strategy and commercial confidentiality.
📄
Built-In NDA Workflow
Digital mutual NDA with timestamped signatures – activated before any sensitive commercial or technical data is exchanged, supporting the confidentiality of your security information.
🔐
Encrypted Document Workspace
AES-256 encryption at rest, TLS in transit, role-based access controls, and full audit trail – ensuring the secure exchange of security questionnaires, specifications and contracts with partners.
🚫
Zero Broker Commission
GTsetu charges zero commission on any partnership formed. All commercial value stays between you and your verified partner.
🌏
Global Network of Verified Partners
Access verified manufacturers, distributors and suppliers across 100+ countries – helping you build a network of partners aligned with your security and compliance expectations.
QWhat is ISO 28000 certification and why is it important?
ISO 28000 is the international standard for Security Management Systems (SMS). The current edition, ISO 28000:2022 “Security and resilience – Security management systems – Requirements”, specifies requirements for establishing, implementing, maintaining and improving a security management system, including aspects relevant to the supply chain. Certification demonstrates that your organisation systematically identifies security-related risks (such as theft, tampering, sabotage and unauthorised access) and controls them. It is increasingly requested by logistics buyers, ports and carriers as evidence of supply chain security maturity, and it is a useful element of partnership evaluation by potential clients.
QWhat are the 5 main steps to get ISO 28000 certified?
The 5 main steps are: (1) Preparation – secure management support, define scope, run a gap analysis and plan the project. (2) Documentation – build the security policy, objectives, security risk assessment and treatment plan, procedures and records. (3) Implementation – roll out controls, train staff and prepare for incidents. (4) Internal Audit & Management Review – verify that the system works and conforms to ISO 28000:2022. (5) Certification Audit – undergo a two-stage audit by an accredited certification body and receive your certificate. This structured approach is similar to building any distributor network – start with a solid foundation and build methodically.
QHow long does it take to get ISO 28000 certification?
The timeline depends on organisation size, number of sites and existing security and quality maturity. As a rough guide, small single-site organisations often take 4–8 months, medium organisations 6–12 months and large multi-site organisations 12 months or more. Organisations that already run ISO 9001, ISO 22301 or ISO 27001 systems can often move faster because ISO 28000:2022 shares the same harmonised structure.
QHow much does ISO 28000 certification cost?
Cost depends on the number of employees, number of sites, the risk profile of your operations and whether you use a consultant. Main components are certification body fees (Stage 1, Stage 2 and annual surveillance audits), consultant or training fees, internal resource time, and any physical or technical security improvements identified during risk assessment. Always obtain written quotes from several accredited certification bodies, as audit-day calculations vary by scope and complexity.
QWhat is the difference between ISO 28000:2007 and ISO 28000:2022?
ISO 28000:2007 focused specifically on security management systems for the supply chain. ISO 28000:2022 is a full revision that adopts the harmonised structure (Annex SL) used by ISO 9001, ISO 14001 and ISO 22301, broadens applicability to all aspects of organisational security, and aligns security risk assessment with ISO 31000 principles. The 2007 edition has been replaced, so certification is now to the 2022 edition.
QWhat documents are required for ISO 28000 certification?
Key documented information includes the security policy, scope of the SMS, security objectives and plans, the security risk assessment and treatment process and results, evidence of competence, operational controls and procedures, emergency preparedness and response plans, monitoring and measurement results, internal audit and management review records, and records of nonconformities and corrective actions. The exact set depends on your organisation – create what is necessary to demonstrate control, and no more. Starting from a proven template can help, much like using a business partnership contract template saves time in legal drafting.
QHow do I choose an ISO 28000 certification body?
Choose a body accredited by a national accreditation body that is a member of the International Accreditation Forum (for example UKAS, ANAB, DAkkS, JAS-ANZ or NABCB), and confirm that ISO 28000 is explicitly within its accredited scope. Check auditor experience in logistics, transport or your industry sector, compare itemised quotes, and confirm that your customers recognise the body’s certificates. The selection process should mirror the rigour you would apply when using partnership evaluation criteria to choose any business partner.
QWhat happens during an ISO 28000 certification audit?
The certification audit is conducted in two stages. Stage 1 (Readiness Review): the auditor reviews your scope, security policy, risk assessment and documented information to confirm the SMS is ready for assessment. Stage 2 (On-Site Assessment): the auditor visits your sites to verify that the system is effectively implemented – interviewing staff, observing operations and reviewing records. If major nonconformities are absent or corrected, the certification body issues your ISO 28000 certificate, normally valid for three years with annual surveillance audits in between.
QCan ISO 28000 be integrated with other ISO management systems?
Yes. ISO 28000:2022 follows the harmonised structure shared by ISO 9001, ISO 14001, ISO 45001, ISO 22301, ISO 27001 and others, so policies, document control, internal audits and management reviews can be combined into one integrated system. See our guides on ISO 14001, ISO 45001 and ISO 22301 to plan an integrated approach.
Connect with verified manufacturers, distributors and suppliers on GTsetu – compliance-backed verification, anonymous discovery, built-in NDA workflows and zero broker commissions. Find partners who share your commitment to security and quality.
They represents the product, and research team behind GTsetu, a global B2B collaboration platform built to help companies explore cross-border partnerships with clarity and trust. The team focuses on simplifying early-stage international business discovery by combining structured company profiles, verification-led access, and controlled collaboration workflows.
With a strong emphasis on trust, and disciplined engagement, Team GTsetu shares insights on global trade, partnerships, and cross-border collaboration, helping businesses make informed decisions before entering deeper commercial discussions.